Proof of Success

Trusted experiences
Clear outcomes
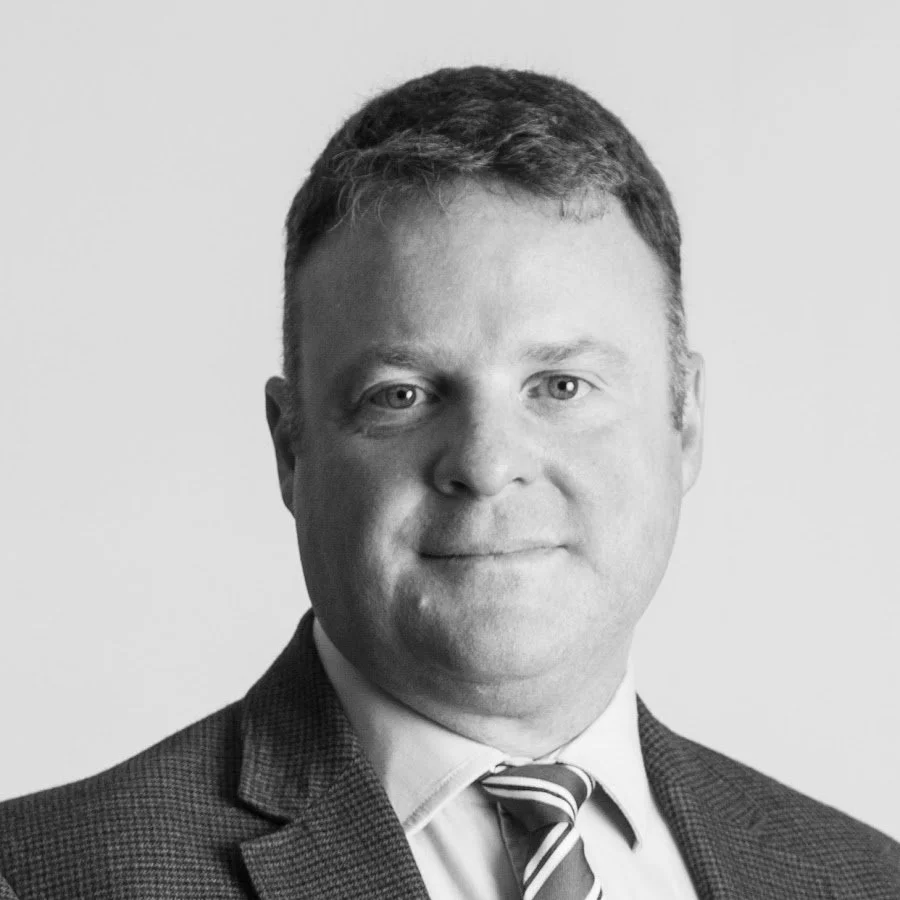
Black and white portrait of a man wearing a suit, tie, and collared shirt.

30+ Years Experience

|

17 Years Metropolitan Police

|

Former Head of Digital Forensics

|

Board-Level Advisor

|

ISO 27001 Lead Auditor

|

International Speaker

|

Twice elected County Councillor and Cabinet Member

|

Member of Local Outbreak Engagement Board (COVID-19 Pandemic)

|

30+ Years Experience | 17 Years Metropolitan Police | Former Head of Digital Forensics | Board-Level Advisor | ISO 27001 Lead Auditor | International Speaker | Twice elected County Councillor and Cabinet Member | Member of Local Outbreak Engagement Board (COVID-19 Pandemic) |

Led by Gary Peace

Redline Advisers is led by Gary Peace — a cross-disciplinary specialist with a background spanning law enforcement investigations, crisis management & planning. Local government and national regulators, anti-corruption, operational governance, incident response, digital forensics, public safety, COVID pandemic response, digital transformation and information security.

That combination is rare. It means a perspective that goes beyond compliance checklists into how organisations actually operate under pressure — where the real risks sit, how decisions are made, and what happens when things go wrong.

Discretion means we don’t name clients. But the pattern of work speaks for itself. Here’s a sample of what we’ve delivered:

Aerospace
ISO27001

Certification rescue, led through first audit with minimal findings in 6 weeks.
Cyber Security
ISO27001

Recertification rescue, delivered with no adverse findings in 4 months.
Certification
Authority

Insider threat mitigation, evidence gathered for senior employee removal in 3 months.
  • "When a cyber attack caused major disruption, the incident response plans Gary had built for us gave us structure at the worst possible moment. As our special advisor, he guided the board from first alert through to recovery — translating complex forensic and legal findings into language management could act on. His calm, informed voice was trusted throughout."

    Transport Supply Chain Provider

  • "After years of IT being driven by one senior individual's preferences rather than the business's needs, we had little visibility of our security posture. Gary acted as our virtual CISO, delivering a calm, impartial maturity review that clearly evidenced the gaps, risks and governance issues. His findings supported both our improvement plan and some difficult but necessary leadership decisions. He gave us the clarity and confidence to move forward."

    Pharma — Virtual CISO

  • "Our ISO 27001 implementation was heading for failure six weeks before our first external audit. Gary stepped in, took control, identified the gaps, and built a pragmatic roadmap we could actually deliver. His calm, decisive approach rescued the project — and we passed."

    Aerospace Firm

  • "Winning a major bank contract meant urgent cyber security and business continuity due diligence under tight deadlines. Gary audited our controls, closed the gaps, wrote the policies we needed, and worked alongside us on the bank's questionnaires. We met every compliance requirement and moved ahead with confidence."

    HR Firm — Banking Due Diligence

  • "Following a breach involving sensitive personal data, Gary stepped in as a DPO-level adviser. He scoped the incident, identified the risks, and led communications with the affected third party — defusing tension and bringing control to a difficult situation. With clear root cause analysis, agreed remediation, and crisis comms support, the third party was satisfied with our response and no further action was taken."

    HR Firm — GDPR Data Breach

  • "Gary and Ben didn't just tick boxes for certification — they helped us build cyber security standards tailored to how we actually work. Thorough, responsive, and always on hand to talk through options. We'd highly recommend ESID."

    UXO Risk Management & Mine Action Specialists

  • "We faced a highly sensitive disciplinary matter involving misuse of IT systems by a senior employee, with serious safeguarding implications. Gary quickly established the facts, advised on evidence and security, and guided us through a clear, defensible process. His calm, objective support gave our leadership team the confidence to act decisively. A huge thank you."

    UK Public Service Provider

  • "Gary's patience and commitment helped safeguard the launch of our challenger bank — a milestone we're all incredibly proud of. He also ran a tabletop exercise for around 70 people across our partner bank's team, and the feedback was stellar. He's amazing."

    Banking – Challenger Bank Launch

  • "Gary delivered a Cyber Incident Response Plan and supporting playbooks that went well above and beyond what we'd envisaged. The review was comprehensive, the uplift genuinely useful, and the documents are now ours to maintain. Exactly what we needed."

    UK Public Service Provider

  • "With three months to recertification, no internal audit completed, and our experienced staff gone, the team had written it off as unachievable. Gary brought structure and momentum from day one — closing process gaps, completing a full internal audit, and building a strong relationship with the external auditors. We passed with no adverse findings."

    Consulting firm – ISO27001 Recertification

Our Principles

A black padlock icon inside a shield, representing security or protection.
An icon of a clock with arrows around it and a wrench in front, representing time management or repair.
A black icon of a stopwatch with motion lines to the left indicating speed or quickness.
Outline of a document with a fingerprint inside a magnifying glass.

Let’s Work Together

The proof is in the work.

If you’d like to discuss how this experience applies to your situation, start with a confidential executive briefing.